An internationally recognized report on your current level of cybersecurity maturity which can be shared with clients, regulators, and government agencies.
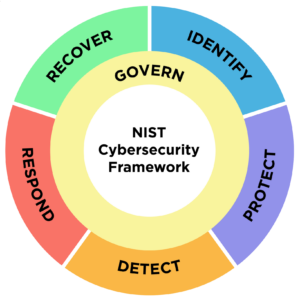
NIST Cybersecurity Framework 2.0
Lead Auditor
Lead Implementor
Photo by ThisisEngineering
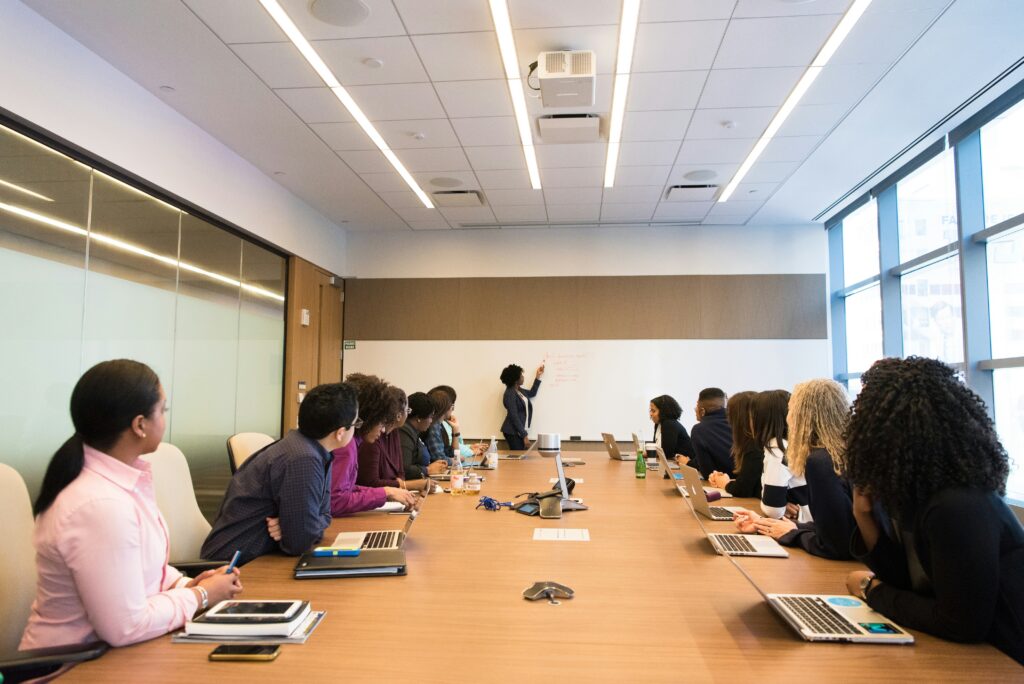
Ensure alignment with leadership team on scope, methodology, and timelines
Photo by Kampus Production
Evaluate technical, operational, and administrative documentation (e.g., risk management framework, policies, regulatory requirements, etc.)
Photo by wocintechchat
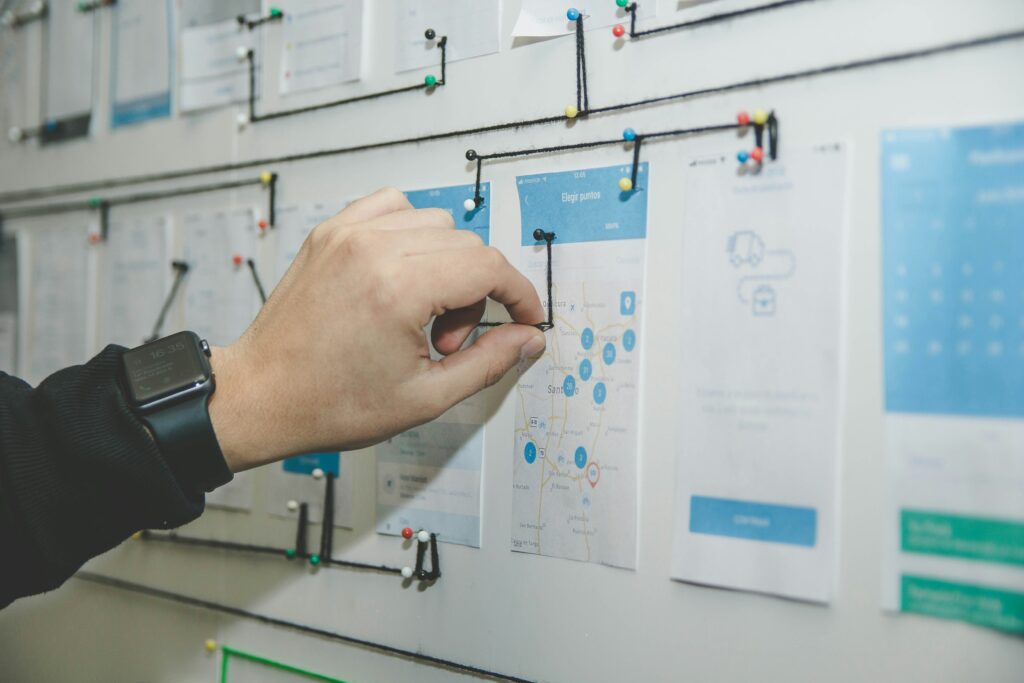
Conduct interviews and workshops across your organization to map critical processes and system dependencies
Photo by brandsandpeople
Compare current controls against NIST CSF requirements and collaborate with your technical teams to identify root causes behind control gaps
Photo by Alvaro Reyes
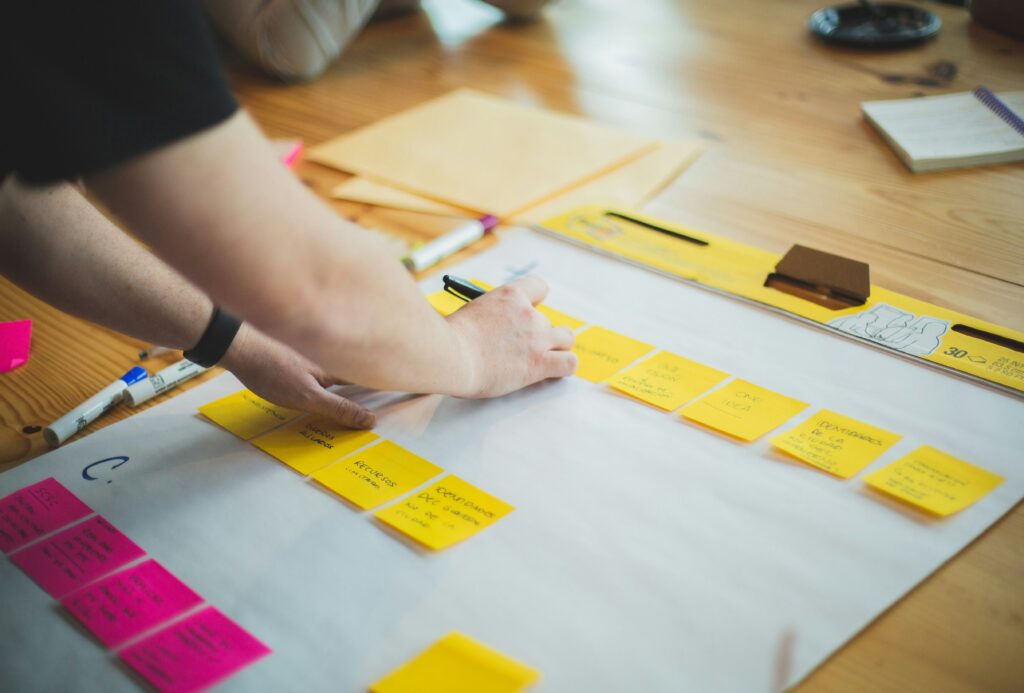
Develop a prioritized, costed plan to better align your organization with the NIST framework
Photo by Loui Kiær
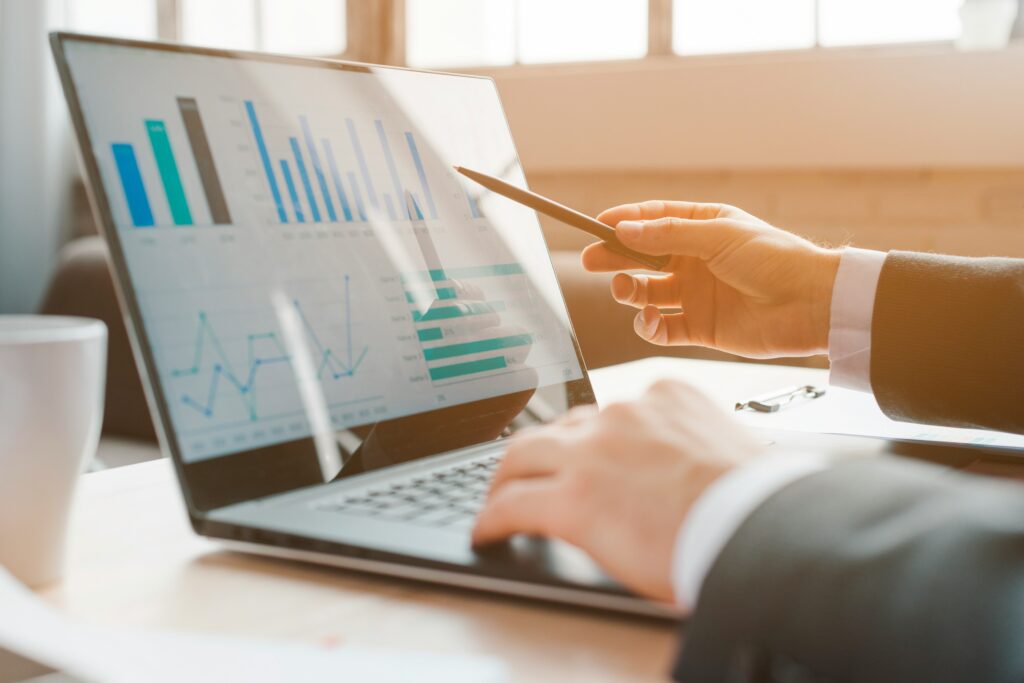
Draft a comprehensive cybersecurity maturity assessment report and review findings with technical and executive leadership